Marcia’s Moving Mouse Revealed Remote Access
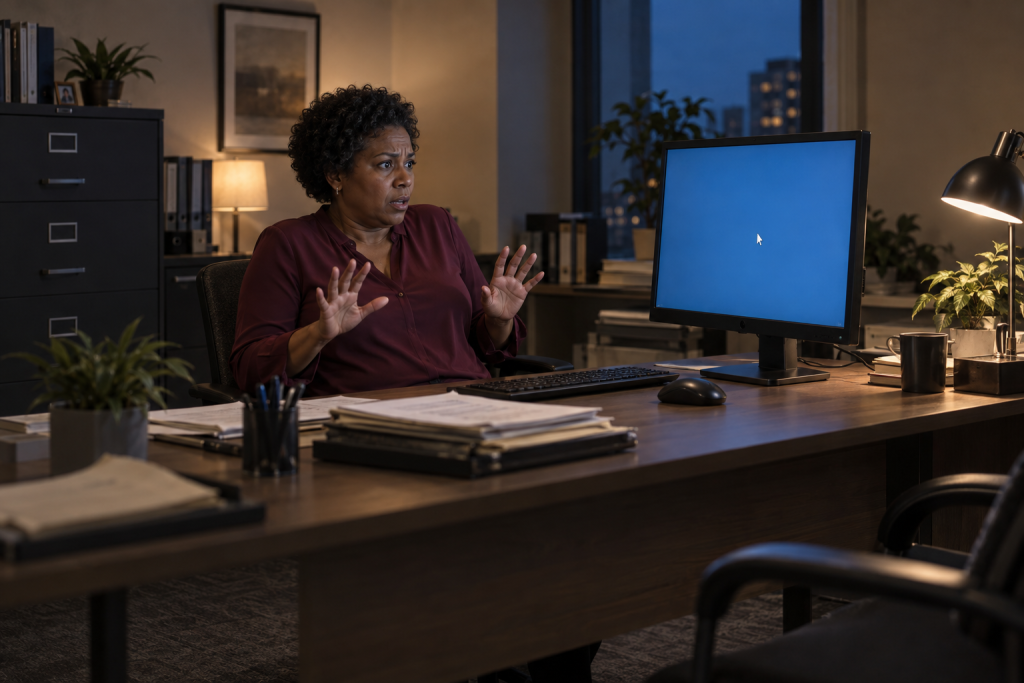
Marcia knew something was wrong when her computer displayed what appeared to be a blue error screen while the mouse continued moving without her control. What initially looked like an unusual Windows problem turned out to be evidence of a serious remote-access intrusion.
A forensic investigation found multiple unauthorized installations of remote-control software. The earliest confirmed activity dated back approximately two months, showing that outsiders had repeatedly accessed the computer without the client’s knowledge.
The likely entry point was a deceptive file that appeared to be connected to an ordinary business proposal. Within moments of that file being opened, remote-access software was installed and began communicating with outside systems.
The intruders later escalated their control by enrolling the computer in a device-management platform belonging to an unrelated outside organization. Systems like this are normally used by businesses to manage employee computers, enforce policies and provide remote support. On Marcia’s computer, none of it was authorized.
The investigation required separating the intruders’ software from legitimate support tools already used by the client. One unfamiliar security component was ultimately confirmed to be legitimate and had only been installed during the previous month. Microsoft Defender’s disabled state was also explained by the presence of Malwarebytes, rather than being treated as proof that the attackers had disabled it.
The unauthorized remote-access installations and management components were removed. Marcia changed all of her passwords, and the computer underwent repeated security checks using extensive system-log collection and cross-referencing tools.
A completely clean Windows installation would ordinarily have provided the greatest certainty. However, the available backup was too old, and wiping the computer risked losing important recent information. Given those circumstances, the best practical solution was to remove the identified threats, preserve the existing system and continue monitoring it closely.
No keylogger, financial theft or confirmed account loss was discovered. The computer returned to service and has undergone extensive scans for the following two weeks without revealing another active threat.
Marcia’s experience demonstrates that an unexplained moving mouse or unfamiliar remote-support icon should never be ignored. Remote access can remain hidden for months, and attackers may install additional management tools designed to preserve their control. Careful investigation is necessary not only to remove what does not belong, but also to avoid mistakenly removing legitimate business and security software.
Related service: Virus, Malware & Browser Cleanup.